Next-generation firewalls
Fortinet and Cisco firewalls, from branch-office appliances to network-core chassis, to secure any type of infrastructure.
Fortinet and Cisco firewalls, from branch-office appliances to network-core chassis, to secure any type of infrastructure.
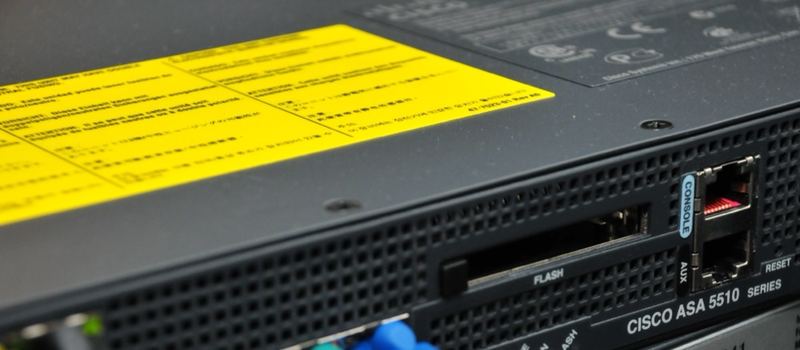
The Cisco ASA 5510 is a network security appliance combining firewall, VPN, and intrusion prevention in a single rack-mountable unit. It was long one of Cisco's reference platforms for securing small and mid-size business Internet access, with dedicated Console and AUX management ports for configuration and remote troubleshooting.
Typical use: Representative of a security gateway installed at the edge of an SME network to filter inbound and outbound Internet traffic and establish VPN tunnels to remote sites.
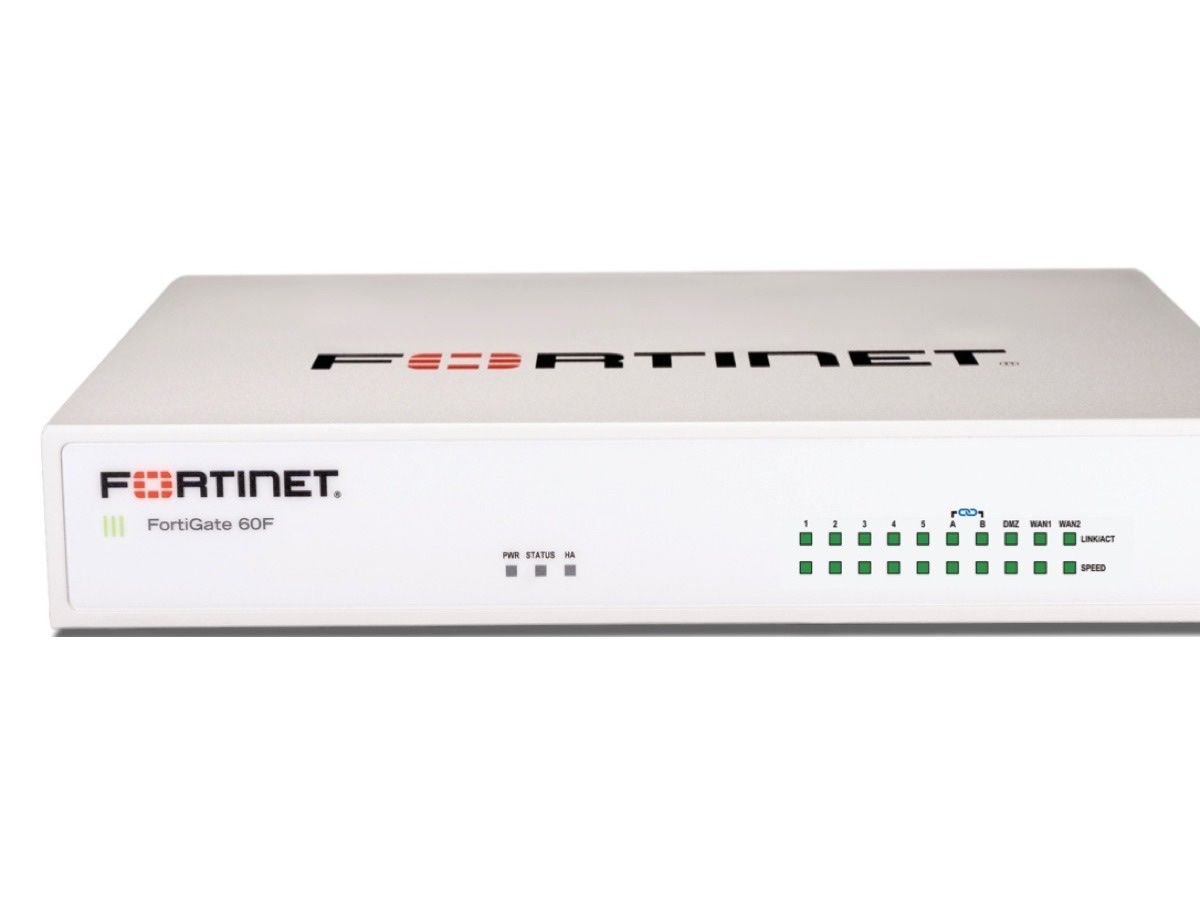
The FortiGate 60F is a compact next-generation firewall from Fortinet built for small businesses and remote branch sites. It combines SD-WAN, VPN, and intrusion prevention in a single desktop appliance, powered by Fortinet's in-house SoC4 security processor. It integrates with the Fortinet Security Fabric for centralized management alongside the rest of the network.
Typical use: Ideal for securing a branch office, retail store, or small office connected to headquarters via VPN/SD-WAN.
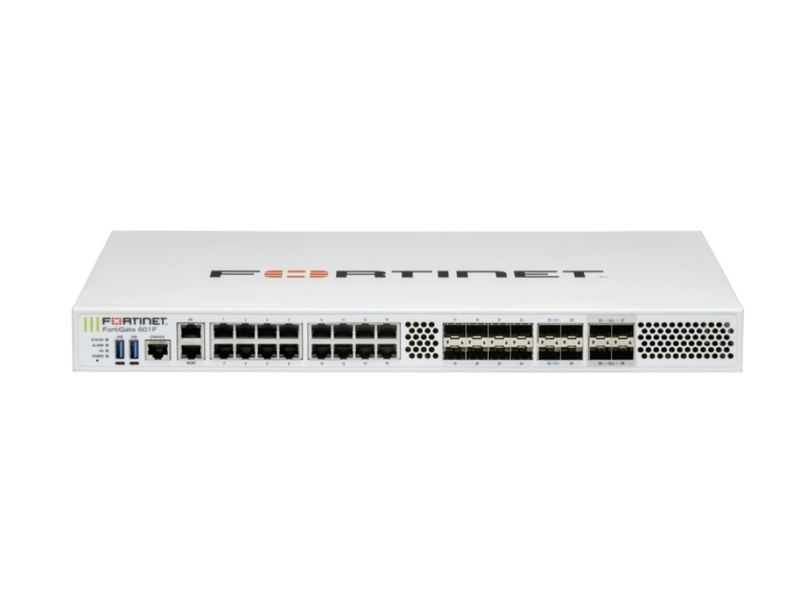
The FortiGate 601F belongs to Fortinet's 600F series, designed for large enterprises and mid-size data centers. This 1U rack-mount firewall delivers high throughput (up to 14 Gbps firewall) through a large set of GE, SFP+, and SFP28 ports for segmenting complex networks. It includes high-performance SSL inspection and AI/ML-powered threat detection from the Fortinet Security Fabric.
Typical use: Suited for protecting the core network of an enterprise or data center that needs high performance and fine-grained segmentation.
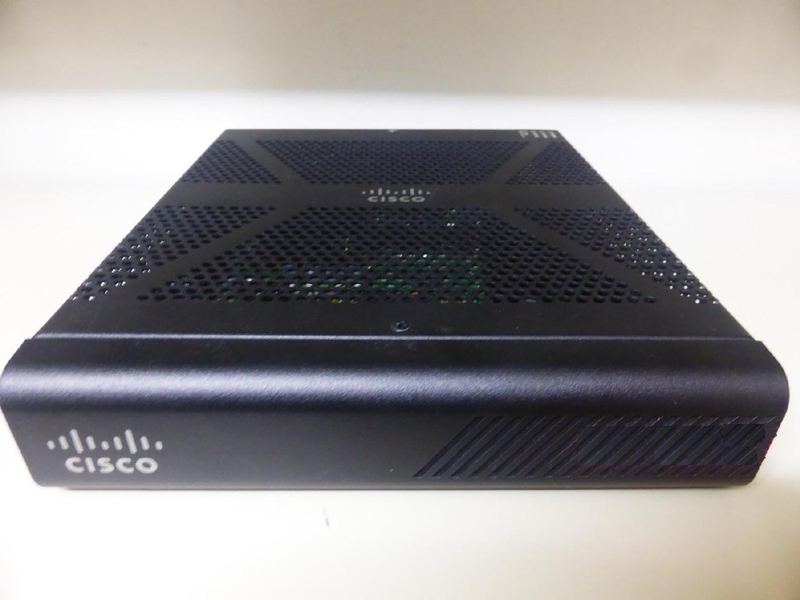
The Cisco ASA 5506-X is a compact security appliance from the ASA 5500-X family, combining a stateful firewall with the FirePOWER module for intrusion prevention, URL filtering, and advanced malware protection (AMP). Designed for small sites and branch offices, it is a newer and more capable alternative to first-generation ASA models. It is managed via Cisco ASDM or the Firepower Management Center.
Typical use: Well suited for securing a small branch or remote office that needs a Cisco firewall with built-in intrusion prevention.
Tell us what you need, and we'll get back to you with a tailored proposal.